Relevance 9/10Importance 9/10
IEEE Spectrum frames the php2shell vulnerability as a wake-up call: AI-assisted analysis is surfacing classes of bugs that have been quietly accumulating in legacy codebases for four decades. The argument is that machine-speed discovery has collapsed the window in which "nobody will ever look at this code" was a viable security strategy. With 479 points, it's the day's clear front-pager.
Relevance 10/10Importance 8/10
A Tell HN post documents that Google trains on personal Gemini chat history even for paying subscribers, with human reviewers able to read transcripts retained up to three years. The only real opt-out is disabling "Keep Activity" — which also nukes your history after 72 hours. Commenters broadly agree it's industry-standard practice, which is arguably the more damning takeaway.
Relevance 9/10Importance 7/10
The RTX Spark laptop (MSI Prestige N16 Flip AI Plus) depends on a Windows-only firmware layer — Nvidia Platform Controllers and Framework — to negotiate CPU/GPU power sharing. Without a Linux equivalent, the GPU throttles to roughly 780 MHz plugged in instead of 2.2 GHz. On GPT-OSS-120B that's about 14 tokens per second on Linux versus 65 on Windows, a 4.6x gap.
Relevance 6/10Importance 10/10
A June supply-chain compromise set the stage; in September, attackers lured a Binance engineer into a fake CEO interview and got him to run malware-laced code that swapped out his legitimate dev tooling. That yielded internal access and credentials, and by October 29 they used a compromised deployment token to drain roughly $6.3 billion. Binance calls it a sophisticated multi-stage campaign, not a one-off phish.
Relevance 9/10Importance 5/10
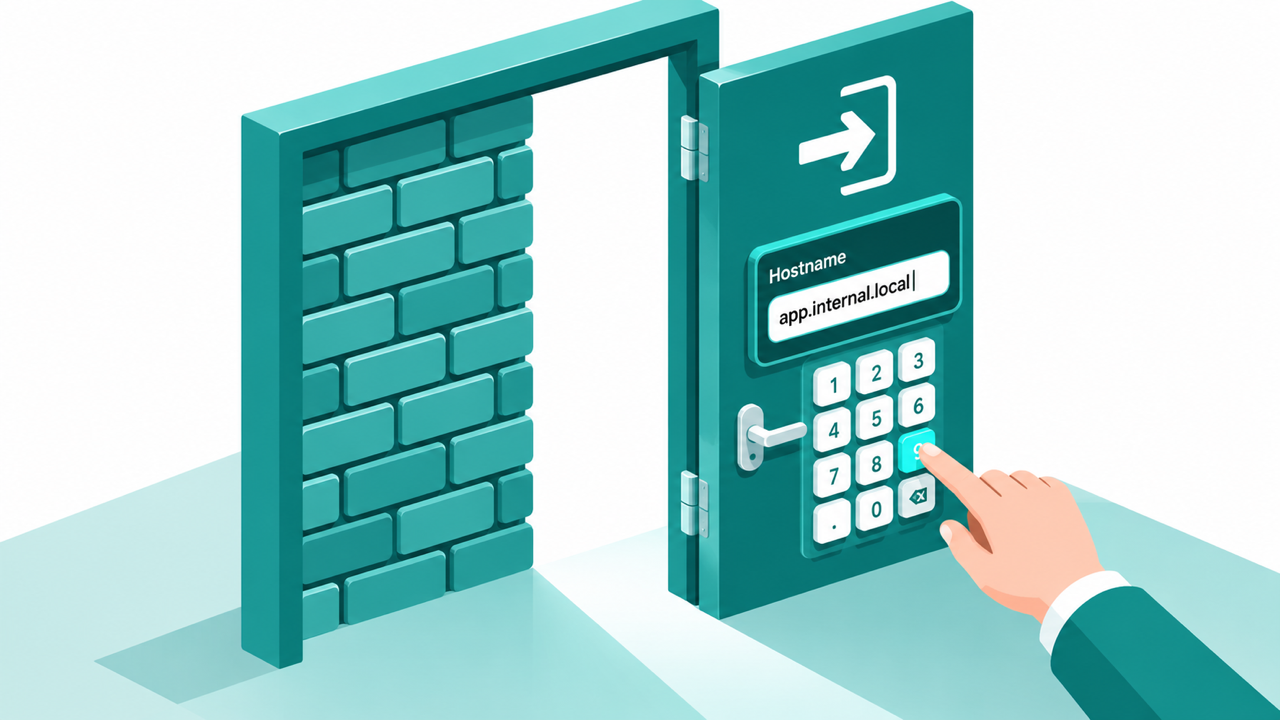
Stream Vessel tackles the MCP OAuth redirect dilemma: a fixed allowlist locks out legitimate custom clients, while accepting arbitrary redirects hands attackers your authorization codes. A May 2026 study found 95.8 percent of tested MCP servers accepted arbitrary redirect URIs from anonymous requesters. Their fix is per-user trusted redirect URIs added at sign-in, capped at ten, requiring the user to type the hostname to confirm.
Relevance 8/10Importance 6/10
Jessica Hullman argues that verifying a result — by AI or by human review — isn't the same as knowing something. Science depends on researchers who can interrogate, defend, and be accountable for findings, and on a community that criticizes them. Optimize purely for AI-generated correct answers and you hollow out the social machinery that turns results into durable knowledge.
Relevance 3/10Importance 9/10
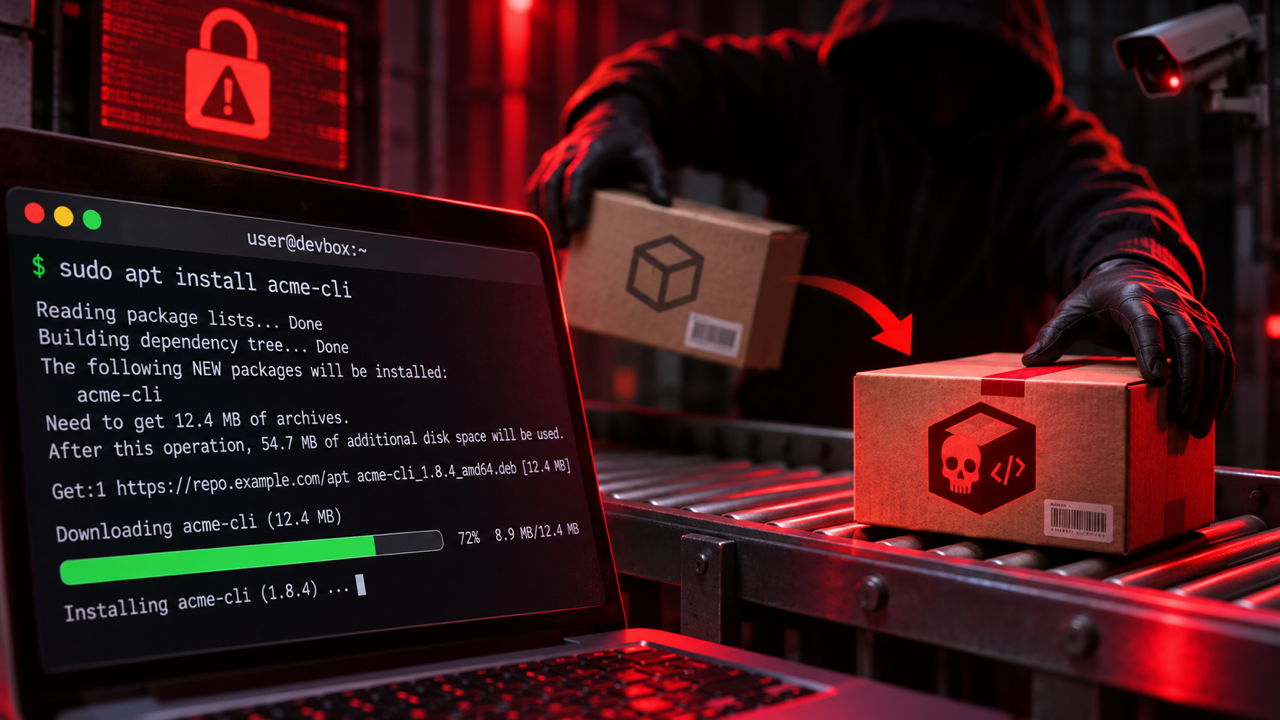
CVE-2026-109518 lets apt merge two distinct package downloads when an HTTP redirect assigns them identical URIs. Combined with sloppy file handling on resumed downloads, a man-in-the-middle can swap a package after verification and get arbitrary code execution as root. Fixed in 3.0.4 for trixie, along with several out-of-bounds access bugs.
Relevance 5/10Importance 6/10
GitHub degraded across Pull Requests, Git operations, Issues, API requests, and Actions starting 09:49 UTC today. Primary mitigation landed at 11:30, Actions recovered by 11:43, and the incident was marked resolved at 11:50 — roughly a two-hour window. A root cause analysis is promised.
Relevance 4/10Importance 5/10
Evergreen is a systems language that folds contracts, invariants, and explicit memory control into one model, with the compiler verifying preconditions, postconditions, and data invariants at build time. The pitch is "more powerful than C, safer than Rust," with proofs erased after verification so runtime performance is untouched. Early days — it landed with 12 points.
Relevance 1/10Importance 3/10
99% Invisible covers San Francisco activists who installed unauthorized bike lane barriers themselves rather than wait out the city's planning process. The city, after initially treating them as illegal, ended up adopting and formalizing the changes. A nice case study in tactical urbanism shipping to prod without a change request.
 HN Briefing AM